INTERPOL + Trend to Fight African Cybercrime Networks
Global threat intelligence helps to disrupt thousands of African cyber crimes networks Read More HERE…

Global threat intelligence helps to disrupt thousands of African cyber crimes networks Read More HERE…
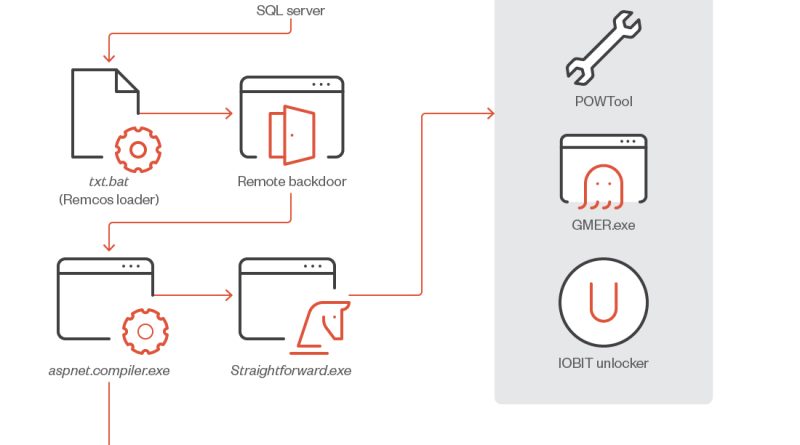
In this entry, we detail our analysis of how the TargetCompany ransomware abused an iteration of fully undetectable (FUD) obfuscator engine BatCloak to infect vulnerable systems. Read More HERE…
We analyze the technical details of a new ransomware family named Big Head. In this entry, we discuss the Big Head ransomware’s similarities and distinct markers that add more technical details to initial reports on the ransomware. Read More HERE…
New uses for generative AI are being introduced every day—but so are new risks. Read More HERE…
This is the third installment of a three-part technical analysis of the fully undetectable (FUD) obfuscation engine BatCloak and SeroXen malware. In this entry, we document the techniques used to spread and abuse SeroXen, as well as the security risks, impact, implications of, and insights into highly evasive FUD batch obfuscators. Read More HERE…
Learn how analysts can search for threats with greater accuracy, speed, and effectiveness. Read More HERE…
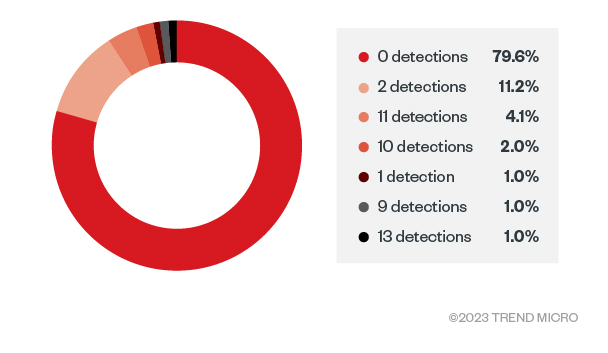
We look into BatCloak engine, its modular integration into modern malware, proliferation mechanisms, and interoperability implications as malicious actors take advantage of its fully undetectable (FUD) capabilities. Read More HERE…
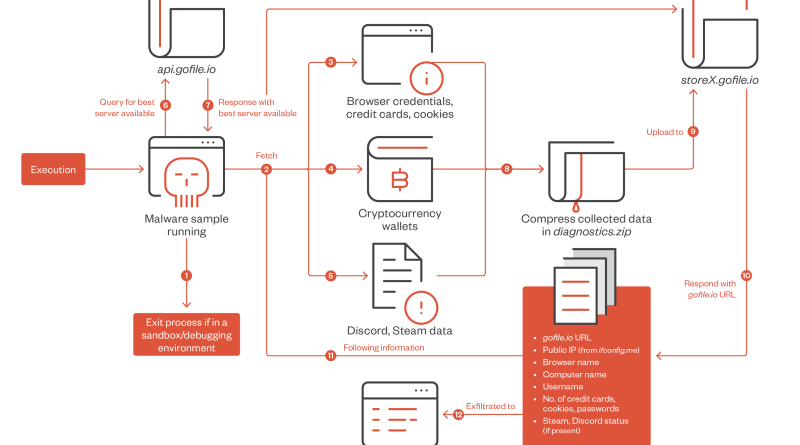
This is the first part of our security analysis of an information stealer targeting GitHub Codespaces (CS) that discusses how attackers can abuse these cloud services for a variety of malicious activities. Read More HERE…
An overview of the Lemon Group’s use of preinfected mobile devices, and how this scheme is potentially being developed and expanded to other internet of things (IoT) devices. This research was presented in full at the Black Hat Asia 2023 Conference in Singapore in May 2023. Read More HERE…