Malware

Microsoft Secure

Star Blizzard refines phishing and malware delivery with the RedFlick technique

Since January 2026, Microsoft has observed Russian state threat actor Star Blizzard evolve their detection evasion capabilities through large-scale phishing campaigns, the use of accounts on compromised websites, and a novel malware delivery technique, tracked by Microsoft as “RedFlick”.
The post Star Blizzard refines phishing and malware delivery with the RedFlick technique appeared first on Microsoft Security Blog. READ MORE HERE…
Read More
Microsoft Secure

NeedyMantis: Unpacking a post-compromise malware family used in targeted operations

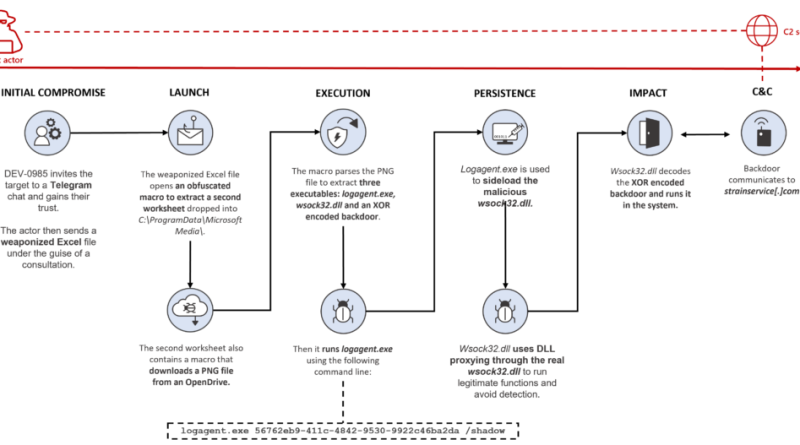
Microsoft Threat Intelligence identified NeedyMantis, a modular post-compromise malware framework used in targeted intrusions that combines custom loaders, encrypted archives, and extensible components to maintain long-term access and support follow-on operations.
The post NeedyMantis: Unpacking a post-compromise malware family used in targeted operations appeared first on Microsoft Security Blog. READ MORE HERE…
Read More
Microsoft Secure

Counterfeit installers to system compromise: Tracking a deceptive software download campaign

An active campaign is impersonating legitimate software vendors to deliver malware through look-alike download pages and regenerated installer archives. Microsoft Defender Experts shares observed attack techniques, Defender XDR detections, indicators of compromise, and practical mitigations to help organizations identify, block, and respond to this threat.
The post Counterfeit installers to system compromise: Tracking a deceptive software download campaign appeared first on Microsoft Security Blog. READ MORE HERE…
Read More
Microsoft Secure

CaptiveCrunch: Midnight Blizzard targets travelers worldwide for malware delivery and credential theft

Storm-2945, a sub-cluster of the Russian threat actor Midnight Blizzard, has been observed compromising the sign-in portals of hospitality-related organizations such as hotels since May 2026 in order to deliver malware to travelers and steal credentials in an operation we call CaptiveCrunch.
The post CaptiveCrunch: Midnight Blizzard targets travelers worldwide for malware delivery and credential theft appeared first on Microsoft Security Blog. READ MORE HERE…

Read More
Microsoft Secure

ACR Stealer: Two observed intrusion chains amid increased threat activity

From late April 2026 to mid-June 2026, Microsoft Defender Experts observed increased ACR Stealer activity across customer environments. These campaigns are successfully using ClickFix lures to steal browser credentials, authentication tokens, and sensitive documents from enterprise environments.
The post ACR Stealer: Two observed intrusion chains amid increased threat activity appeared first on Microsoft Security Blog. READ MORE HERE…

Read More