Security

Networkworld

IBM z16: A mainframe designed for AI, hybrid cloud, security and open source

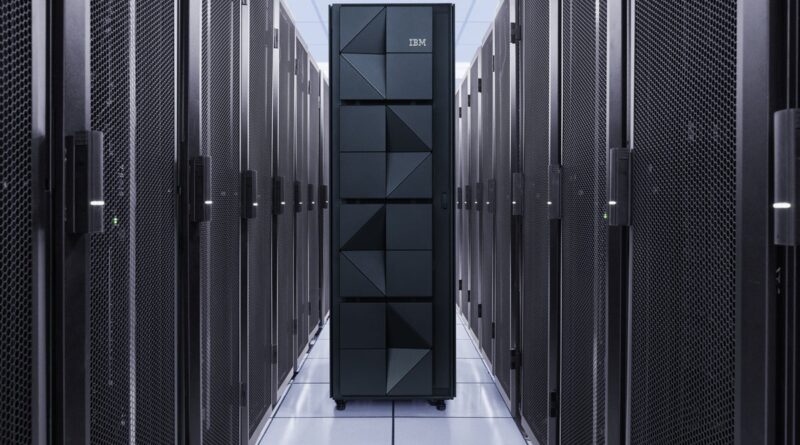
Today’s announcement of IBM’s new z16 mainframes promises a system that caters to enterprise needs that include support for AI, security, hybrid cloud, and open source efforts well into the future.The new, more powerful and feature-rich Big Iron boasts an AI accelerator built onto its core Telum processor that can do 300 billion deep-learning inferences per day with one millisecond latency and includes what IBM calls a quantum-safe system to protect organizations from anticipated quantum-based security threats.
[Get regularly scheduled insights by signing up for Network World newsletters.]To read this article in full, please click here READ MORE HERE…
Read More
Networkworld

Fortinet tightens integration of enterprise security, networking controls

Fortinet has made available a new release of its core FortiOS software that includes features the vendor says will help enterprises more tightly meld security and networking controls.FortiOS 7.2, has 300 new features including AI support to help stop network threats more quickly, sandboxing to help fight ransomware threats, and improved SD-WAN, branch, and edge orchestration.How to choose an edge gateway
FortiOS is the vendor’s operating system for the FortiGate family of hardware and virtual components. FortiOS implements Fortinet Security Fabric and includes network security such as firewalling, access control, and authentication in addition to SD-WAN, switching, and wireless services. To read this article in full, please click here READ MORE HERE…
Read More
Networkworld

Use zero trust to fight network technical debt

Zero trust (ZT) is a mindset and a method, not a technology. The current push to adopt ZT is driven by an urgent and growing need to make a major leap forward in risk management and attack containment in enterprise networks, a need driven home by every successive wave of ransomware. IT can use the urgency of moving to ZT to root out some of the technical debt in the environment. Specifically, it can be a catalyst to find areas exempted from network and network security standards and bring them up to date under the new paradigm of zero trust.No more exempting network components from access-control roles
In a ZT environment, the network not only doesn’t trust a node new to it, but it also doesn’t trust nodes that are already communicating across it. When a node is first seen by a ZT network, the network will require that the node go through some form of authentication and authorization check. Does it have a valid certificate to prove its identity? Is it allowed to be connected where it is based on that identity? Is it running valid software versions, defensive tools, etc.? It must clear that hurdle before being allowed to communicate across the network.To read this article in full, please click here READ MORE HERE…
Read More
Networkworld

IBM service aims to secure multicloud operations

IBM is launching a new service to help customers manage their data encryption keys in a hybrid cloud environment. Unified Key Orchestrator lets customers integrate all security key-management systems into one managed service that’s backed by Big Blue’s Hardware Security Module. HSM is IBM’s system that protects against physical or logical attacks and has special hardware to perform cryptographic operations and protect keys.Gartner: IT skills shortage hobbles cloud, edge, automation growth
Available from IBM Cloud, Unified Key Orchestrator lets customers maintain visibility and control over who has access to their critical data, while running workloads across hybrid or multicloud cloud environments. In addition, with a single, secure, cloud-based  view of an organization’s crypto keys, enterprises can create and revoke keys for their data across multiple clouds. At the same time, companies no longer need to rely on security experts with specialized knowledge of each individual cloud to handle security operations, according to IBM.To read this article in full, please click here READ MORE HERE…
Read More
Networkworld

What is NAC and why is it important for network security?

Network Access Control (NAC) is a cybersecurity technique that prevents unauthorized users and devices from entering private networks and accessing sensitive resources. Also known as Network Admission Control, NAC first gained a foothold in the enterprise in the mid-to-late 2000s as a way to manage endpoints through basic scan-and-block techniques.As knowledge workers became increasingly mobile, and as BYOD initiatives spread across organizations, NAC solutions evolved to not only authenticate users, but also to manage endpoints and enforce policies.How NAC works
NAC tools detect all devices on the network and provide visibility into those devices. NAC software prevents unauthorized users from entering the network and enforces policies on endpoints to ensure devices comply with network security policies. NAC solutions will, for instance, make sure that the endpoint has up-to-date antivirus and anti-malware protections.To read this article in full, please click here READ MORE HERE…
Read More
Networkworld

Gartner: SSE is SASE minus the SD-WAN

SASE adoption has been skyrocketing since the start of the pandemic. Secure access service edge, a term Gartner coined in 2019, combines security and networking in a single, scalable, cloud-based platform that fits well in a world in which employees work from home and mostly access cloud-based apps and services.Now Gartner is pushing a new acronym. Turns out, companies might prefer to get their SASE without the “A” — just security service edge, or SSE. Gartner this month published a Magic Quadrant for SSE (something the company never did for SASE); it’s available from vendors listed in the report (here and here, for example).To read this article in full, please click here READ MORE HERE…
Read More
Networkworld

Cisco IDs top 2022 security threats and what to do about them

2022 will be another busy year for enterprise incident responders as ransomware, supply chain and myriad zero-day attacks will continue to rise, according to Cisco’s Talos security experts.To help address the threats, the Cisco Talos team used a blog and online presentation to detail steps enterprises can take to defend themselves against the growing field of bad actors and also to point out lessons learned from recent damaging exploits such as the Log4j vulnerability and Microsoft Exchange server zero-day threats.Once, zero-day attacks were typically launched by state actors against service providers, but those days are gone, wrote Nick Biasini head of outreach at Cisco Talos in a blog about the security landscape in 2022. Now new, less experienced combatants seek out a broader range of targets, using less surgical attacks. “This has led to more risky behavior than we’ve seen historically, without as much regard for collateral damage,” he wrote.To read this article in full, please click here READ MORE HERE…
Read More