
Security

Networkworld

IBM tweaks its z14 mainframe to make it a better physical fit for the data center

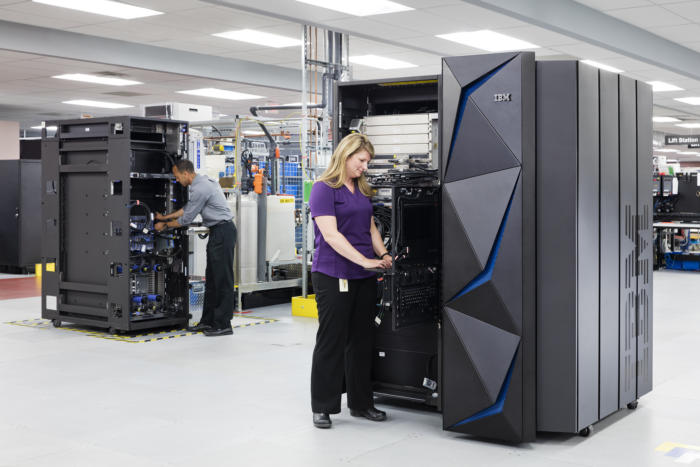
IBM is widening its mainframe range with some narrower models – ZR1 and Rockhopper II – that are skinny enough to fit in a standard 19-inch rack, which will answer criticisms of potential customers that the hulking z14 introduced in July 2017 too big to fit in their data centers (see photo above).In addition to new, smaller, packaging for its z14 hardware, IBM is also introducing Secure Service Container technology. This makes use of the z14’s encryption accelerator and other security capabilities to protect containerized applications from unwanted interference.[ Check out REVIEW: VMware’s vSAN 6.6 and hear IDC’s top 10 data center predictions . | Get regularly scheduled insights by signing up for Network World newsletters. ]
When IBM introduced the z14 last July, with an accelerator to make encrypting information standard practice in the data center, there was one problem: The mainframe’s two-door cabinet was far too deep and too wide to fit in standard data center aisles.To read this article in full, please click here READ MORE HERE…
Read More
Networkworld

Network-as-a-Service: A modern solution to today’s networking challenges

Traditional networking architectures over the past two decades or so prescribe that the hub of the network be build around a specific location, such as a data center or a company’s headquarters building.This location houses most of the equipment for compute, storage, communications, and security, and this is where enterprise applications are traditionally hosted. For people in branch and other remote locations, traffic is typically backhauled to this hub before going out to other locations, including to the cloud.[ Don’t miss customer reviews of top remote access tools. | Get daily insights by signing up for Network World newsletters. ]To read this article in full, please click here READ MORE HERE…
Read More
Networkworld

Tips to improve IoT security on your network

Judging by all the media attention that The Internet of Things (or IoT) gets these days, you would think that the world was firmly in the grip of a physical and digital transformation. The truth, though, is that we all are still in the early days of the IoT.The analyst firm Gartner, for example, puts the number of Internet connected “things” at just 8.4 billion in 2017 – counting both consumer and business applications. That’s a big number, yes, but much smaller number than the “50 billion devices” or “hundreds of billions of devices” figures that get bandied about in the press.To read this article in full, please click here(Insider Story) READ MORE HERE…

Read More
Networkworld

How to eliminate the default route for greater security

If portions of enterprise data-center networks have no need to communicate directly with the internet, then why do we configure routers so every system on the network winds up with internet access by default?Part of the reason is that many enterprises use an internet perimeter firewall performing port address translation (PAT) with a default policy that allows access the internet, a solution that leaves open a possible path by which attackers can breach security.+Also on Network World: IPv6 deployment guide; What is edge computing and how it’s changing the network?+To read this article in full, please click here(Insider Story) READ MORE HERE…

Read More
Networkworld

5 Ways to Secure Wi-Fi Networks

Wi-Fi is one entry-point hackers can use to get into your network without setting foot inside your building because wireless is much more open to eavesdroppers than wired networks, which means you have to be more diligent about security.But there’s a lot more to Wi-Fi security than just setting a simple password. Investing time in learning about and applying enhanced security measures can go a long way toward better protecting your network. Here are six tips to betters secure your Wi-Fi network.Use an inconspicuous network name (SSID)
The service set identifier (SSID) is one of the most basic Wi-Fi network settings. Though it doesn’t seem like the network name could compromise security, it certainly can. Using a too common of a SSID, like “wireless” or the vendor’s default name, can make it easier for someone to crack the personal mode of WPA or WPA2 security. This is because the encryption algorithm incorporates the SSID, and password cracking dictionaries used by hackers are preloaded with common and default SSIDs. Using one of those just makes the hacker’s job easier.To read this article in full, please click here READ MORE HERE…
Read More
Networkworld

IoT privacy: 30 ways to build a security culture

Much work still must be done before the industrial and municipal Internet of Things (IoT) becomes widely adopted outside of the circle of innovators. One field, privacy, well understood by the public and private sector in the context of the cloud, PCs and mobile, is in the early stage of adaptation for the IoT.The sheer volume of data that will be collected and the new more granular architecture of the IoT present new privacy concerns that need to be resolved on an equal scale as the platform’s forecasted growth.A demonstration of this new aspect of privacy and compliance is the Privacy Guidelines for Internet of Things: Cheat Sheet, Technical Report (pdf) by Charith Perera, researcher at the Newcastle University in the U.K. The nine-page report details 30 points about implementing strong privacy protections. This report is summarized below.To read this article in full, please click here READ MORE HERE…
Read More
Networkworld

Unix: How random is random?

On Unix systems, random numbers are generated in a number of ways and random data can serve many purposes. From simple commands to fairly complex processes, the question “How random is random?” is worth asking.EZ random numbers
If all you need is a casual list of random numbers, the RANDOM variable is an easy choice. Type “echo $RANDOM” and you’ll get a number between 0 and 32,767 (the largest number that two bytes can hold).$ echo $RANDOM
29366

Of course, this process is actually providing a “pseudo-random” number. As anyone who thinks about random numbers very often might tell you, numbers generated by a program have a limitation. Programs follow carefully crafted steps, and those steps aren’t even close to being truly random. You can increase the randomness of RANDOM’s value by seeding it (i.e., setting the variable to some initial value). Some just use the current process ID (via $$) for that. Note that for any particular starting point, the subsequent values that $RANDOM provides are quite predictable.To read this article in full, please click here READ MORE HERE…
Read More
Networkworld

The complexity of password complexity

Deploying password quality checking on your Debian-base Linux servers can help to ensure that your users assign reasonable passwords on their accounts, but the settings themselves can be a bit misleading. For example, setting a minimum password length of 12 characters does not mean that your users’ passwords will all have twelve or more characters. Let’s stroll down Complexity Boulevard and see how the settings work and examine some settings worth considering.First, if you haven’t done this already, install the password quality checking library with this command:apt-get -y install libpam-pwquality

The files that contain most of the settings we’re going to look at will be:To read this article in full, please click here READ MORE HERE…
Read More
Networkworld

Gravityscan, keeping WordPress sites safe

If your website, in common with roughly 25% of all websites, is running WordPress then it’s pretty much certain that it’s being constantly attacked. WordPress is to hackers what raw meat is to jackals because unless sites are assiduously maintained, they quickly become vulnerable to a huge number of exploits.The root cause of this vulnerability is WordPress’ ecosystem of complex core software augmented by thousands of third party developers whose themes and plugins are often buggy and not quickly (or often, never) updated to fend off known security problems. Add to that many site owners being slow to update their core WordPress installation and you have an enormous and easily discovered collection of irresistible hacking targets.To read this article in full, please click here READ MORE HERE…
Read More
Networkworld

8 ways to manage an internet or security crisis

Your business is hit with a ransomware attack. Or your ecommerce site crashes. Your legacy system stops working. Or maybe your latest software release has a major bug. These are just some of the problems that ecommerce, technology and other companies experience at one time or another.The issue is not if a problem – or crisis – occurs, but how your company handles it when it does. Manage the problem poorly, you risk losing customers, or worse. Handle a crisis promptly and professionally, you can fend off a public relations disaster and might even gain new customers.So what steps can businesses take to mitigate and effectively manage an IT-related crisis? Here are eight suggestions.To read this article in full, please click here READ MORE HERE…
Read More