
Research

PRC-linked spies hid inside medical and military networks for more than a year, snooping through Gmail and stealing data
Google says the intruders were on the hunt for everything from drone tech to pathogens READ MORE HERE…
Risks in Telecommunications IT Sr. Threat Researcher Sr. Threat Researcher Sr. Threat Researcher Manager, Threat Research
We summarize the characteristics, threats, and recommendations to improve the security posture of enterprises’ and telecommunications companies’ IT infrastructure. Read More HERE…
Threat Actors Exploit Misconfigured Apache Hadoop YARN Sr. Security Researcher Threat Researcher
We look into how threat actors are exploiting Apache Hadoop YARN, a part of the Hadoop framework that is responsible for executing tasks on the cluster. This analysis covers the payloads deployed, the tactics used in the attacks, and basic recommendations for strengthening cloud security. Read More HERE…
StrongPity APT Group Deploys Android Malware for the First Time Sr. Threat Researcher Mobile Threats Analyst
We recently conducted an investigation into a malicious Android malware sample, which we believe can be attributed to the StrongPity APT group, that was posted on the Syrian e-Gov website. To the best of our knowledge, this is the first time that the group has been publicly observed using malicious Android applications as part of its attacks. Read More HERE…
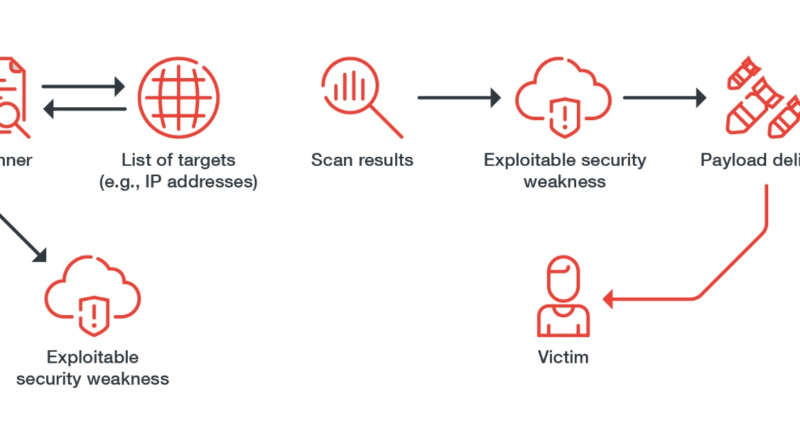
TeamTNT Campaigns Emphasize Importance of Addressing Cloud Security Gaps Trend Micro
Having covered TeamTNT in several of our blog entries over the past couple of years, we embarked on a research that encompasses the malicious actor group’s campaigns, tools, and techniques in 2020 and early 2021. Read More HERE…
Main Considerations for Securing Enterprise 5G Networks
5G brings countless benefits to enterprises through its scalability, speed, and connectivity. However, these very same features might actually amplify the damage caused by threats if they do infiltrate systems. Security should be a prime concern for enterprises that use 5G networks. Read More HERE…
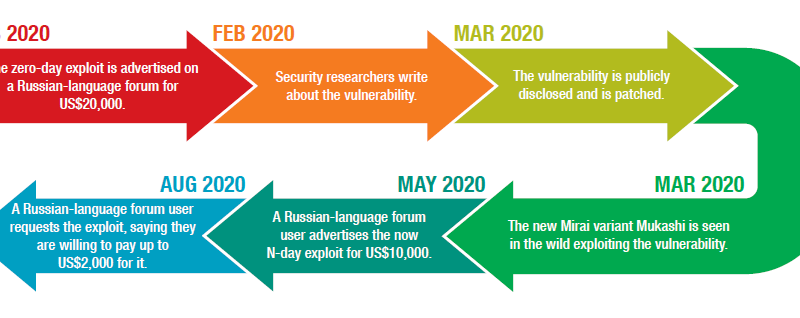
The Underground Exploit Market and the Importance of Virtual Patching Trend Micro
Over the past two calendar years, we conducted research on the underground exploit market to learn more about the life cycle of exploits, the kinds of buyers and sellers who transact, and the business models that are in effect in the underground. Read More HERE…