Linux

Microsoft Secure

Cookie-controlled PHP webshells: A stealthy tradecraft in Linux hosting environments

Cookie-gated PHP webshells use obfuscation, php-fpm execution, and cron-based persistence to evade detection in Linux hosting environments. This post examines how this tradecraft conceals execution behind specially crafted HTTP cookies.
The post Cookie-controlled PHP webshells: A stealthy tradecraft in Linux hosting environments appeared first on Microsoft Security Blog. READ MORE HERE…

Read More
Microsoft Secure

Mitigating the Axios npm supply chain compromise

On March 31, 2026, the popular HTTP client Axios experienced a supply chain attack, causing two newly published npm packages for version updates to download from command and control (C2) that Microsoft Threat Intelligence has attributed to the North Korean state actor Sapphire Sleet. Although the malicious versions are no longer available for download, since Axios is one of the most widely used HTTP clients in the JavaScript ecosystem, this compromise exposed hundreds to potentially millions of users.
The post Mitigating the Axios npm supply chain compromise appeared first on Microsoft Security Blog. READ MORE HERE…

Read More
Microsoft Secure

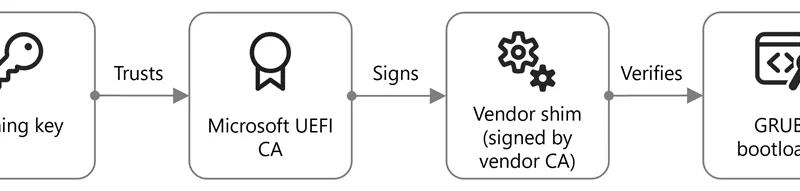
Analyzing open-source bootloaders: Finding vulnerabilities faster with AI

Using Microsoft Security Copilot to expedite the discovery process, Microsoft has uncovered several vulnerabilities in multiple open-source bootloaders impacting all operating systems relying on Unified Extensible Firmware Interface (UEFI) Secure Boot. Through a series of prompts, we identified and refined security issues, ultimately uncovering an exploitable integer overflow vulnerability in the GRUB2, U-boot, and Barebox bootloaders.
The post Analyzing open-source bootloaders: Finding vulnerabilities faster with AI appeared first on Microsoft Security Blog. READ MORE HERE…

Read More
Networkworld

20th National Cybersecurity Awareness Month kicks off

As National Cybersecurity Awareness Month kicks off, it’s a good time to reflect on how secure the systems you manage are – whether they’re running Linux, Windows or some other OS. While Linux is considered by many to be more secure due to its open-source nature and because privileges are clearly defined, it still warrants security reviews, and this month’s focus on cybersecurity awareness suggests that an annual review is more than just a good idea.The designation became official in 2004, when President George W. Bush and Congress declared October to be National Cybersecurity Awareness Month. Keep in mind that in 2004, security practice often involved little more than updating antivirus software. Today, cybersecurity practices are much more intense as the threats have grown to be far more significant and far more challenging.To read this article in full, please click here READ MORE HERE…

Read More
Microsoft Secure

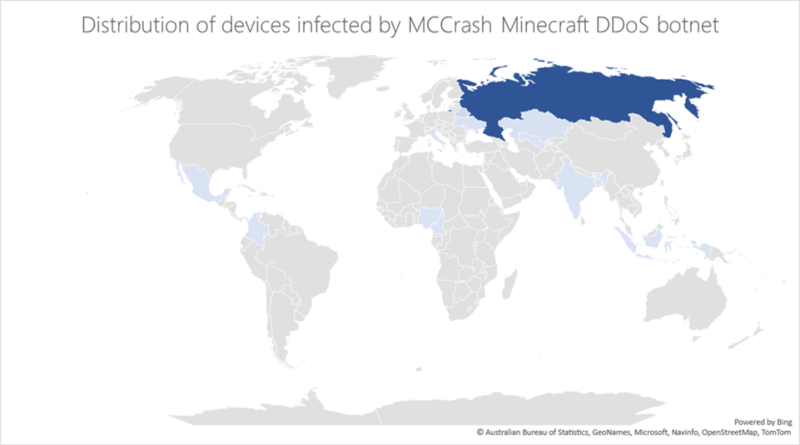
MCCrash: Cross-platform DDoS botnet targets private Minecraft servers

The Microsoft Defender for IoT research team analyzed a cross-platform botnet that infects both Windows and Linux systems from PCs to IoT devices, to launch distributed denial of service (DDoS) attacks against private Minecraft servers.
The post MCCrash: Cross-platform DDoS botnet targets private Minecraft servers appeared first on Microsoft Security Blog. READ MORE HERE…

Read More
Microsoft Secure

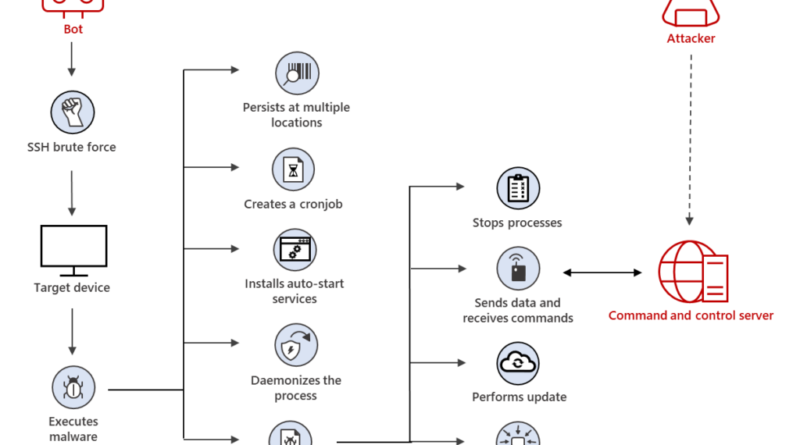
Rise in XorDdos: A deeper look at the stealthy DDoS malware targeting Linux devices

Observing a 254% increase in activity over the last six months from a versatile Linux trojan called XorDdos, the Microsoft 365 Defender research team provides in-depth analysis into this stealthy malware’s capabilities and key infection signs.
The post Rise in XorDdos: A deeper look at the stealthy DDoS malware targeting Linux devices appeared first on Microsoft Security Blog. READ MORE HERE…

Read More
Microsoft Secure

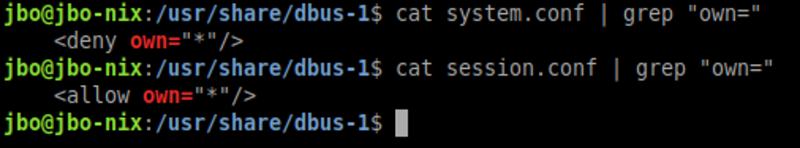
Microsoft finds new elevation of privilege Linux vulnerability, Nimbuspwn

Microsoft has discovered several vulnerabilities, collectively referred to as Nimbuspwn, that could be chained together, allowing an attacker to elevate privileges to root on many Linux desktop endpoints. Leveraging Nimbuspwn as a vector for root access could allow attackers to achieve greater impact on vulnerable devices by deploying payloads and performing other malicious actions via arbitrary root code execution.
The post Microsoft finds new elevation of privilege Linux vulnerability, Nimbuspwn appeared first on Microsoft Security Blog. READ MORE HERE…

Read More
Networkworld

Feds’ demand for software standards could boost enterprise security

Enterprises can look for more transparency from software vendors after the Biden Administration’s recent mandate that software bills of materials be provided by companies attempting to do business with the federal government.Software bills of materials, frequently abbreviated to SBOMs, aren’t a new concept. The idea comes from the manufacturing sector, where it’s often crucial for buyers to fully understand the components and materials that were used to make a particular piece of equipment.The 10 most powerful companies in enterprise networking 2021
For example, a train engine might contain parts that aren’t rated for certain levels of vibration stress, making it unsuitable for use on a particular type of track. The goal of an SBOM is similar, listing all the proprietary, open source, and licensed components being used in a particular piece of software, so that a buyer can review it and check whether any of those components are outdated or insecure.To read this article in full, please click here READ MORE HERE…

Read More
Networkworld

How to enforce password complexity on Linux

Deploying password-quality checking on your Debian-based Linux servers can help ensure that your users assign reasonably secure passwords to their accounts, but the settings themselves can be a bit misleading.For example, setting a minimum password length of 12 characters does not necessarily mean that all your users’ passwords will actually have 12 or more characters.Let’s stroll down Complexity Boulevard and see how the settings work and examine some that are worth considering.[Get regularly scheduled insights by signing up for Network World newsletters.]
The files that contain the settings we’re going to look at will be:To read this article in full, please click here READ MORE HERE…

Read More