Windows

Microsoft Secure

DeadLock ransomware: Breaking down a Rust-based encryptor with decentralized recovery infrastructure

Microsoft Threat Intelligence examines DeadLock ransomware, an emerging financially motivated operation distinguished by its use of decentralized infrastructure to support victim communications, negotiations, and data leak operations alongside double extortion tactics used to pressure victims.
The post DeadLock ransomware: Breaking down a Rust-based encryptor with decentralized recovery infrastructure appeared first on Microsoft Security Blog. READ MORE HERE…
Read More
Microsoft Secure

CaptiveCrunch: Midnight Blizzard targets travelers worldwide for malware delivery and credential theft

Storm-2945, a sub-cluster of the Russian threat actor Midnight Blizzard, has been observed compromising the sign-in portals of hospitality-related organizations such as hotels since May 2026 in order to deliver malware to travelers and steal credentials in an operation we call CaptiveCrunch.
The post CaptiveCrunch: Midnight Blizzard targets travelers worldwide for malware delivery and credential theft appeared first on Microsoft Security Blog. READ MORE HERE…
Read More
Microsoft Secure

Mitigating the Axios npm supply chain compromise

On March 31, 2026, the popular HTTP client Axios experienced a supply chain attack, causing two newly published npm packages for version updates to download from command and control (C2) that Microsoft Threat Intelligence has attributed to the North Korean state actor Sapphire Sleet. Although the malicious versions are no longer available for download, since Axios is one of the most widely used HTTP clients in the JavaScript ecosystem, this compromise exposed hundreds to potentially millions of users.
The post Mitigating the Axios npm supply chain compromise appeared first on Microsoft Security Blog. READ MORE HERE…
Read More
Microsoft Secure

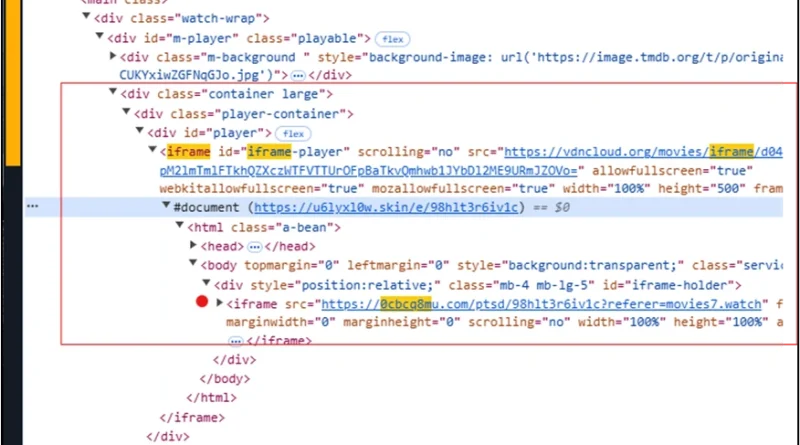
WhatsApp malware campaign delivers VBS payloads and MSI backdoors

A malware campaign uses WhatsApp messages to deliver VBS scripts that initiate a multi-stage infection chain. The attack leverages renamed Windows tools and cloud-hosted payloads to install MSI backdoors and maintain persistent access to compromised systems.
The post WhatsApp malware campaign delivers VBS payloads and MSI backdoors appeared first on Microsoft Security Blog. READ MORE HERE…
Read More
Microsoft Secure

WhatsApp malware campaign delivers VBScript and MSI backdoors

A malware campaign uses WhatsApp messages to deliver VBS scripts that initiate a multi-stage infection chain. The attack leverages renamed Windows tools and cloud-hosted payloads to install MSI backdoors and maintain persistent access to compromised systems.
The post WhatsApp malware campaign delivers VBScript and MSI backdoors appeared first on Microsoft Security Blog. READ MORE HERE…

Read More
Microsoft Secure

Cyber Signals Issue 9 | AI-powered deception: Emerging fraud threats and countermeasures

Microsoft maintains a continuous effort to protect its platforms and customers from fraud and abuse. This edition of Cyber Signals takes you inside the work underway and important milestones achieved that protect customers.
The post Cyber Signals Issue 9 | AI-powered deception: Emerging fraud threats and countermeasures appeared first on Microsoft Security Blog. READ MORE HERE…

Read More
Microsoft Secure

Threat actors misuse Node.js to deliver malware and other malicious payloads

Since October 2024, Microsoft Defender Experts has observed and helped multiple customers address campaigns leveraging Node.js to deliver malware and other payloads that ultimately lead to information theft and data exfiltration.
The post Threat actors misuse Node.js to deliver malware and other malicious payloads appeared first on Microsoft Security Blog. READ MORE HERE…

Read More
Microsoft Secure

Analyzing open-source bootloaders: Finding vulnerabilities faster with AI

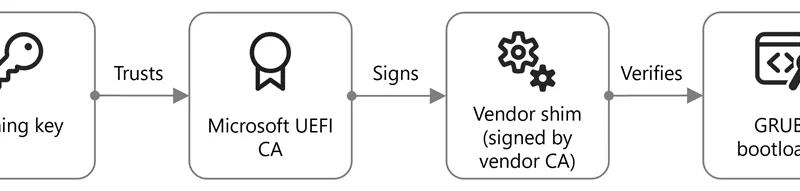
Using Microsoft Security Copilot to expedite the discovery process, Microsoft has uncovered several vulnerabilities in multiple open-source bootloaders impacting all operating systems relying on Unified Extensible Firmware Interface (UEFI) Secure Boot. Through a series of prompts, we identified and refined security issues, ultimately uncovering an exploitable integer overflow vulnerability in the GRUB2, U-boot, and Barebox bootloaders.
The post Analyzing open-source bootloaders: Finding vulnerabilities faster with AI appeared first on Microsoft Security Blog. READ MORE HERE…

Read More
Microsoft Secure

Malvertising campaign leads to info stealers hosted on GitHub

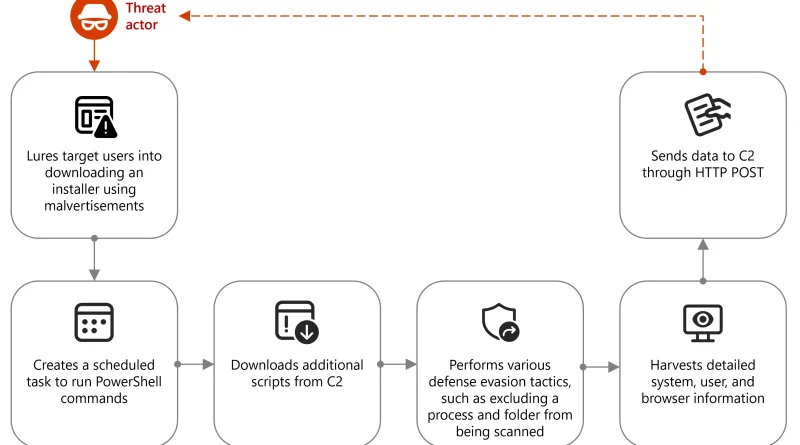
Microsoft detected a large-scale malvertising campaign in early December 2024 that impacted nearly one million devices globally. The attack originated from illegal streaming websites embedded with malvertising redirectors and ultimately redirected users to GitHub to deliver initial access payloads as the start of a modular and multi-stage attack chain.
The post Malvertising campaign leads to info stealers hosted on GitHub appeared first on Microsoft Security Blog. READ MORE HERE…

Read More
Microsoft Secure

Microsoft’s guidance to help mitigate Kerberoasting  

Kerberoasting, a well-known Active Directory (AD) attack vector, enables threat actors to steal credentials and navigate through devices and networks. Microsoft is sharing recommended actions administrators can take now to help prevent successful Kerberoasting cyberattacks.
The post Microsoft’s guidance to help mitigate Kerberoasting   appeared first on Microsoft Security Blog. READ MORE HERE…

Read More