This Week in Security News – September 10, 2021 VP, Threat Intelligence
Biden announces cybersecurity initiative partnership, US Government seeks public feedback on draft federal zero trust strategy and more. Read More HERE…

Biden announces cybersecurity initiative partnership, US Government seeks public feedback on draft federal zero trust strategy and more. Read More HERE…
Microsoft has disclosed the existence of a new zero-day vulnerability that affects multiple versions of Windows. This vulnerability (designated as CVE-2021-40444) is currently delivered via malicious Office 365 documents and requires user input to open the file to trigger. Read More HERE…
The announcement marks the US’s extensive collaboration with various private and education sector leaders to address the rising cyber threats in the country. Read More HERE…
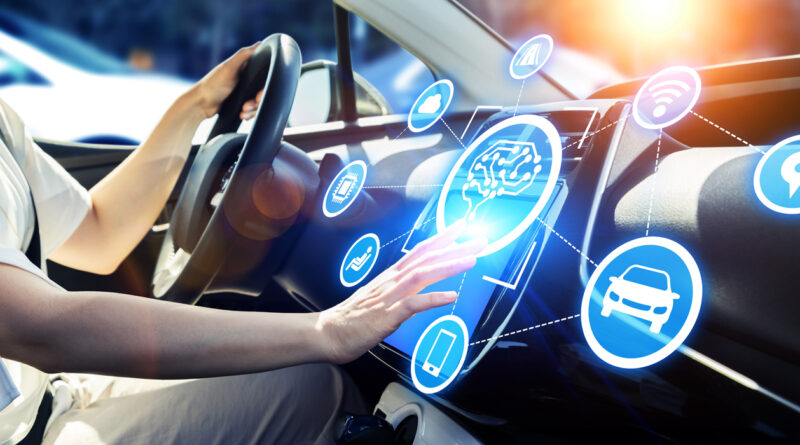
The collaboration aims to enhance various features on GM’s connected cars, with the hope of having millions of vehicles with 5G connectivity on the road by 2024. Read More HERE…
Proxytoken vulnerability can modify Exchange server configs and Lockbit jumps its own countdown, publishes Bangkok Air files Read More HERE…
The United Nations Regulation No. 155 sets requirements for cybersecurity in vehicles. We conducted a threat modelling exercise on its defined attack vectors as a form of risk assessment in order to help organizations comply with this regulation and identify what to prioritize. Read More HERE…

The latest version comes weeks after US President Biden announced a memo, calling on the improvement of control systems cybersecurity. It also expands the coverage of previous editions, covering all control systems. Read More HERE…
Key takeaways from H1’ 2021 Linux threat report and Google removes fake crypto-mining apps and more. Read More HERE…
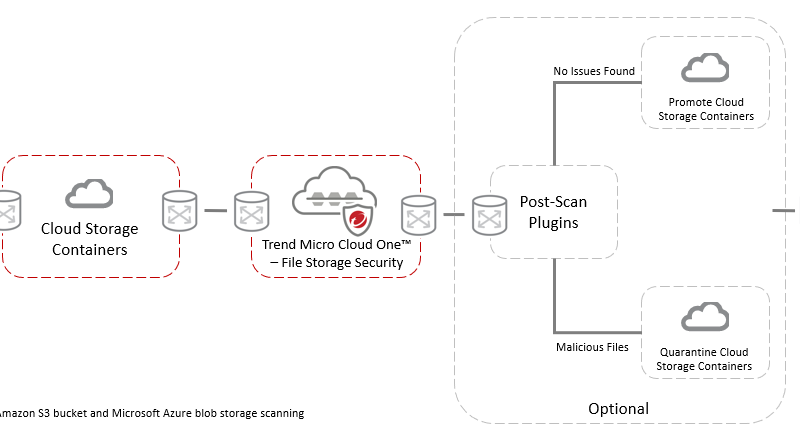
New on the Trend Micro Cloud One security platform: Learn how easy it is to monitor, identify, and quarantine malicious file entering your Azure Blobs. Read More HERE…