PHP 8.6: Things are gonna get a lot more strict around here
Like a parent disciplining a misbehaving child, PHP’s annual update clamps down on loose default behaviors to curb malicious hacker horseplay. READ MORE HERE…

Like a parent disciplining a misbehaving child, PHP’s annual update clamps down on loose default behaviors to curb malicious hacker horseplay. READ MORE HERE…

READ MORE HERE…
Read More
READ MORE HERE…
Read More
READ MORE HERE…
Read MoreSANS offers cyber security pros a valuable toolkit of resources to mitigate the potentially serious cybersecurity risks faced by internal staff Sponsored Post Organisations that fail to adequately address the potential vulnerabilities that internal employees sometimes encounter when developing an IT security strategy are exposing themselves to potentially catastrophic dangers, infosec experts have warned.… READ MORE HERE…
Read More
AI-generating malware, deep fake identity spoofing, and state-sponsored ransomware are just a few of the latest methods that attackers are using to bypass traditional cybersecurity tools. Ritesh Agrawal, CEO of cybersecurity startup Airgap Networks, noticed that many of the attacks that compromise enterprise networks fail to penetrate telco and service provider networks.“Even though they’re deploying the same routers, switches, and firewalls, there’s something fundamentally different about telco networks that shields them from many threats to enterprise LANs,” Argawal said. Agrawal has 20 years of experience with cybersecurity, enterprise networking, and cloud computing, most of that time spent with Juniper Networks focusing on telco and large enterprise clients.To read this article in full, please click here READ MORE HERE…
Read MoreIt’s time to think about whether we need a new and improved approach to global cybersecurity.
READ MORE HERE…
Guidelines and tools designed to help organizations strengthen their cyber posture will be rendered useless if rules aren’t in place to ensure such practices are adopted.
READ MORE HERE…
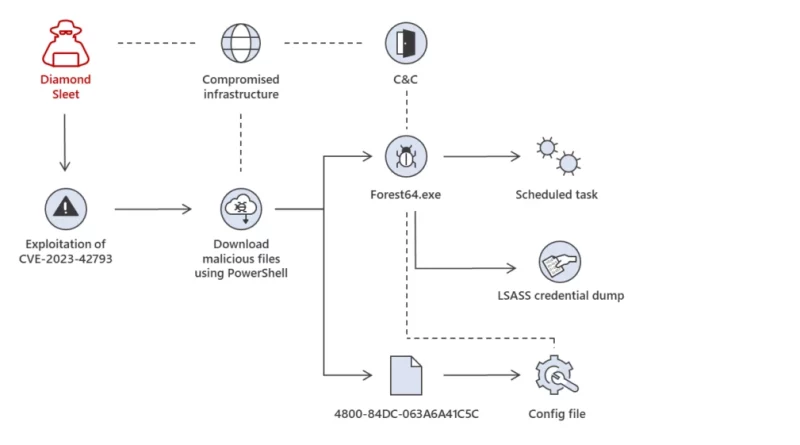
Since early October 2023, Microsoft has observed North Korean nation-state threat actors Diamond Sleet and Onyx Sleet exploiting the Jet Brains TeamCity CVE-2023-42793 remote-code execution vulnerability. Given supply chain attacks carried out by these threat actors in the past, Microsoft assesses that this activity poses a particularly high risk to organizations who are affected.
The post Multiple North Korean threat actors exploiting the TeamCity CVE-2023-42793 vulnerability appeared first on Microsoft Security Blog. READ MORE HERE…