PHP 8.6: Things are gonna get a lot more strict around here
Like a parent disciplining a misbehaving child, PHP’s annual update clamps down on loose default behaviors to curb malicious hacker horseplay. READ MORE HERE…

Like a parent disciplining a misbehaving child, PHP’s annual update clamps down on loose default behaviors to curb malicious hacker horseplay. READ MORE HERE…
Sure, we’re waking to the risk, but we gotta get outta bed, warns Endor Labs founder Varun Badhwar interview The more cybersecurity news you read, the more often you seem to see a familiar phrase: Software supply chain (SSC) vulnerabilities. Varun Badhwar, founder and CEO at security firm Endor Labs, doesn’t believe that’s by coincidence. … READ MORE HERE…
Read MoreBad configurations, insecure versions of jQuery, and crummy cookies are some of myriad problems Exclusive Five Chinese researchers examined the configurations of nearly 14,000 government websites across the country and found worrying lapses that could lead to malicious attacks, according to a not-yet-peer-reviewed study released last week.… READ MORE HERE…
Read More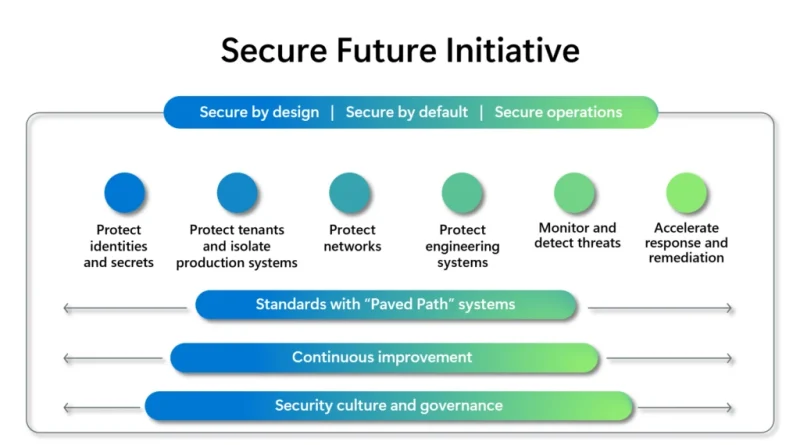
Microsoft is expanding the scope of the Secure Future Initiative to adapt to the evolving cyberthreat landscape. Read about the principles and pillars driving this initiative.
The post Security above all else—expanding Microsoft’s Secure Future Initiative appeared first on Microsoft Security Blog. READ MORE HERE…

READ MORE HERE…
Read MoreREAD MORE HERE…
Read MoreCops prevented crims from bilking victims out of more than €10m – but couldn’t stop crime against art A Europol-led operation dubbed “Pandora” has shut down a dozen phone scam centers, and arrested 21 suspects. The cops reckon the action prevented criminals from bilking victims out of more than €10 million (£8.6 million, $11 million).… READ MORE HERE…
Read MoreGoogle Account users have authenticated themselves using passkeys more than 1 billion times, but passwords are likely to be around for years.
READ MORE HERE…
Warning comes exactly a year after the vulnerability was introduced The US Cybersecurity and Infrastructure Security Agency (CISA) is forcing all federal agencies to patch a critical vulnerability in GitLab’s Community and Enterprise editions, confirming it is very much under “active exploit.”… READ MORE HERE…
Read More