UK government can’t keep its encryption-busting order to Apple a secret, tribunal rules
Notice’s existence can be acknowledged without harming national security, but its precise demands remain under wraps READ MORE HERE…

Notice’s existence can be acknowledged without harming national security, but its precise demands remain under wraps READ MORE HERE…
It seems like scammers are everywhere these days. Here are two new ways Google aims to tackle the problem on Android.READ MORE HERE…
Read MoreAkira really wasn’t horsing around with this one Toronto Zoo’s final update on its January 2024 cyberattack arrived this week, revealing that visitor data going back to 2000 had been compromised.… READ MORE HERE…
Read More
The Aqara Camera Hub G5 Pro blends home security with hub functionality, offering AI-powered visual recognition – no subscription required.READ MORE HERE…
Read More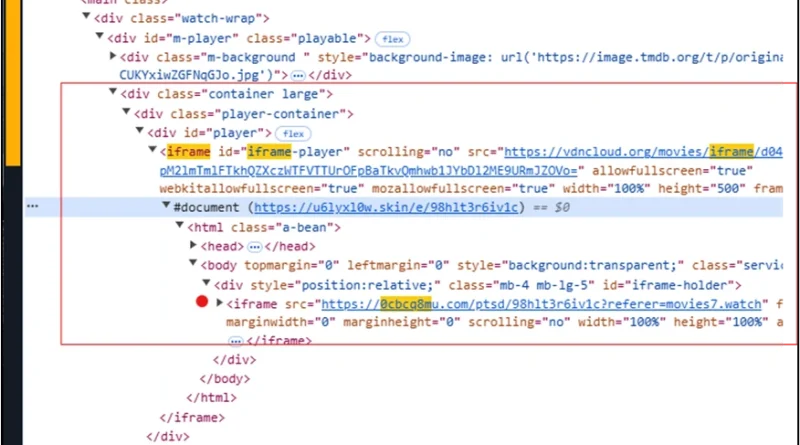
Microsoft detected a large-scale malvertising campaign in early December 2024 that impacted nearly one million devices globally. The attack originated from illegal streaming websites embedded with malvertising redirectors and ultimately redirected users to GitHub to deliver initial access payloads as the start of a modular and multi-stage attack chain.
The post Malvertising campaign leads to info stealers hosted on GitHub appeared first on Microsoft Security Blog. READ MORE HERE…
Complaint alleges 13 funding proposals foundered amid battle for control Eric Gan is no longer CEO of AI security biz Cybereason after what appears to have been a protracted and unpleasant fight with investors, including the SoftBank Vision Fund and Liberty Strategic Capital.… READ MORE HERE…
Read MoreLooking for a router that can provide full, convenient VPN coverage at home? These are the best routers that support VPN installation or include pre-installed software.READ MORE HERE…
Read More
A first-of-its-kind legal challenge set to be heard this month, per reports Updated Apple has reportedly filed a legal complaint with the UK’s Investigatory Powers Tribunal (IPT) contesting the British government’s order that it must forcibly break the encryption of iCloud data.… READ MORE HERE…
Read MoreThey’re good at zero-day exploits, too Silk Typhoon, the Chinese government crew believed to be behind the December US Treasury intrusions, has been abusing stolen API keys and cloud credentials in ongoing attacks targeting IT companies and state and local government agencies since late 2024, according to Microsoft Threat Intelligence.… READ MORE HERE…
Read More
Silk Typhoon is a Chinese state actor focused on espionage campaigns targeting a wide range of industries in the US and throughout the world. In recent months, Silk Typhoon has shifted to performing IT supply chain attacks to gain access to targets. In this blog, we provide an overview of the threat actor along with insight into their recent activity as well as their longstanding tactics, techniques, and procedures (TTPs), including a persistent interest in the exploitation of zero-day vulnerabilities in various public-facing appliances and moving from on-premises to cloud environments.
The post Silk Typhoon targeting IT supply chain appeared first on Microsoft Security Blog. READ MORE HERE…
Hunters International ready to off-shore 1.4 TB of info allegedly swiped from Indian giant A subsidiary of Indian multinational Tata has allegedly fallen victim to the notorious ransomware gang Hunters International.… READ MORE HERE…
Read More