
Microsoft Secure

Microsoft Secure

CaptiveCrunch: Midnight Blizzard targets travelers worldwide for malware delivery and credential theft

Storm-2945, a sub-cluster of the Russian threat actor Midnight Blizzard, has been observed compromising the sign-in portals of hospitality-related organizations such as hotels since May 2026 in order to deliver malware to travelers and steal credentials in an operation we call CaptiveCrunch.
The post CaptiveCrunch: Midnight Blizzard targets travelers worldwide for malware delivery and credential theft appeared first on Microsoft Security Blog. READ MORE HERE…
Read More
Microsoft Secure

Enhancing AI security through global AI red teaming

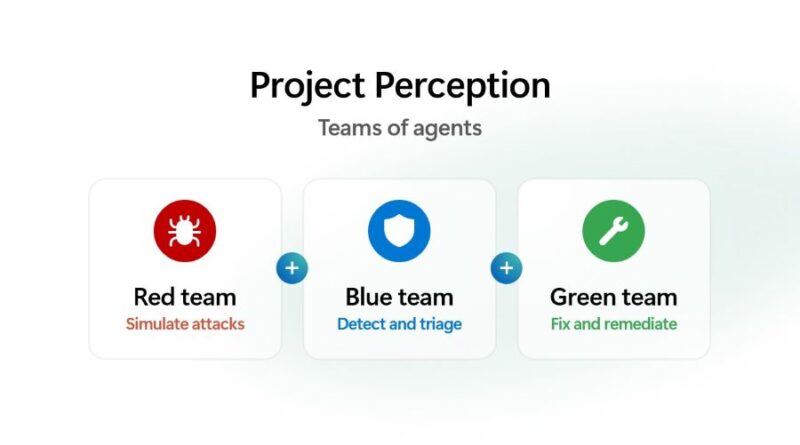
Microsoft’s External Red Team Alliance (EXTRA) is a global AI security initiative designed to advance AI safety research and red teaming. By partnering with universities, researchers, and regional experts, EXTRA helps identify emerging AI risks, improve security testing, and strengthen the resilience of frontier AI systems.
The post Enhancing AI security through global AI red teaming appeared first on Microsoft Security Blog. READ MORE HERE…
Read More
Microsoft Secure

Email threat landscape: Q2 2026 trends and insights

In the second quarter of 2026, the continuing effects of Microsoft’s disruption of the Tycoon2FA phishing platform contributed to sustained declines in several major phishing techniques, while threat actors expanded into Teams-based social engineering and employed increasingly automated and multi-stage attack chains.
The post Email threat landscape: Q2 2026 trends and insights appeared first on Microsoft Security Blog. READ MORE HERE…
Read More
Microsoft Secure

ACR Stealer: Two observed intrusion chains amid increased threat activity

From late April 2026 to mid-June 2026, Microsoft Defender Experts observed increased ACR Stealer activity across customer environments. These campaigns are successfully using ClickFix lures to steal browser credentials, authentication tokens, and sensitive documents from enterprise environments.
The post ACR Stealer: Two observed intrusion chains amid increased threat activity appeared first on Microsoft Security Blog. READ MORE HERE…
Read More